> For the complete documentation index, see [llms.txt](https://docs.plenit.com/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.plenit.com/docs-en/productos/servers/how-to/vpn-logs-and-troubleshooting.md).
# How to Manage Your VPN Logs and Diagnose Issues
The troubleshooting console lets you **generate, view, and download** the VPN tunnel logs from the panel, and diagnose most issues yourself.
The key is to read the log to know **at which phase** the connection fails.
> #### 👍 What you get
>
> Locate the exact point of failure (the initial connection or the data transfer) and the action that fixes it, without relying on support in most cases.
### Before you start
* Have access to the panel with permissions on the network subscription.
* Have a VPN tunnel created, whether operational or not.
* Optionally, access to the remote machine logs to correlate if you need to go further.
### Step 1. Generate and view the logs
1. Go to your Servers subscription and open the tab **VPN**.
2. On the tunnel, open its ⋮ menu and click **Generate log**.
3. In the console you can **view** the exchange events, **search** terms, **copy** snippets and **download** the file `.log` to review it locally.
Recommended search terms: `error`, `failed`, `proposal`, `AUTH`, `TS_`, `CHILD_SA`, `responding`.
Tunnel menu in the VPN tab with the Generate log option
> #### 📘 Two details to avoid confusion
>
> * **Time zone**: logs show the time converted to your time zone, so the timestamp matches the actual moment of the test and you can compare it with the remote machine log.
> * **Size-based rotation**: the history is managed by size, not by days. If you are tracking a specific failure, reproduce it and generate the logs right after.
### The two phases of the connection
A site-to-site tunnel comes up in two phases. Knowing which one fails takes you straight to the cause.
#### Phase 1 — Initial connection (IKE)
The two endpoints validate each other and agree how they will communicate. When all goes well, the log shows `IKE_SA ... established`. If it fails, it is usually because the other endpoint does not respond (connectivity or closed ports), basic settings do not match (for example, encryption), or the key (PSK) or identity do not match.
#### Phase 2 — Data transfer (IPsec / CHILD\_SA)
With the initial connection ready, the tunnel through which the actual traffic travels is created. When all goes well, it shows `CHILD_SA ... established`. If it fails, it is usually because the subnets do not match on both sides, a firewall or policy blocks the traffic, or there are missing routes to the remote network.
> #### 📘 Quick rule
>
> If you see `IKE_SA ... established` but not `CHILD_SA ... established`, the problem is in networks, routes, or firewall (Phase 2). If you do not get to `IKE_SA ... established`, it is in the initial connection (Phase 1).
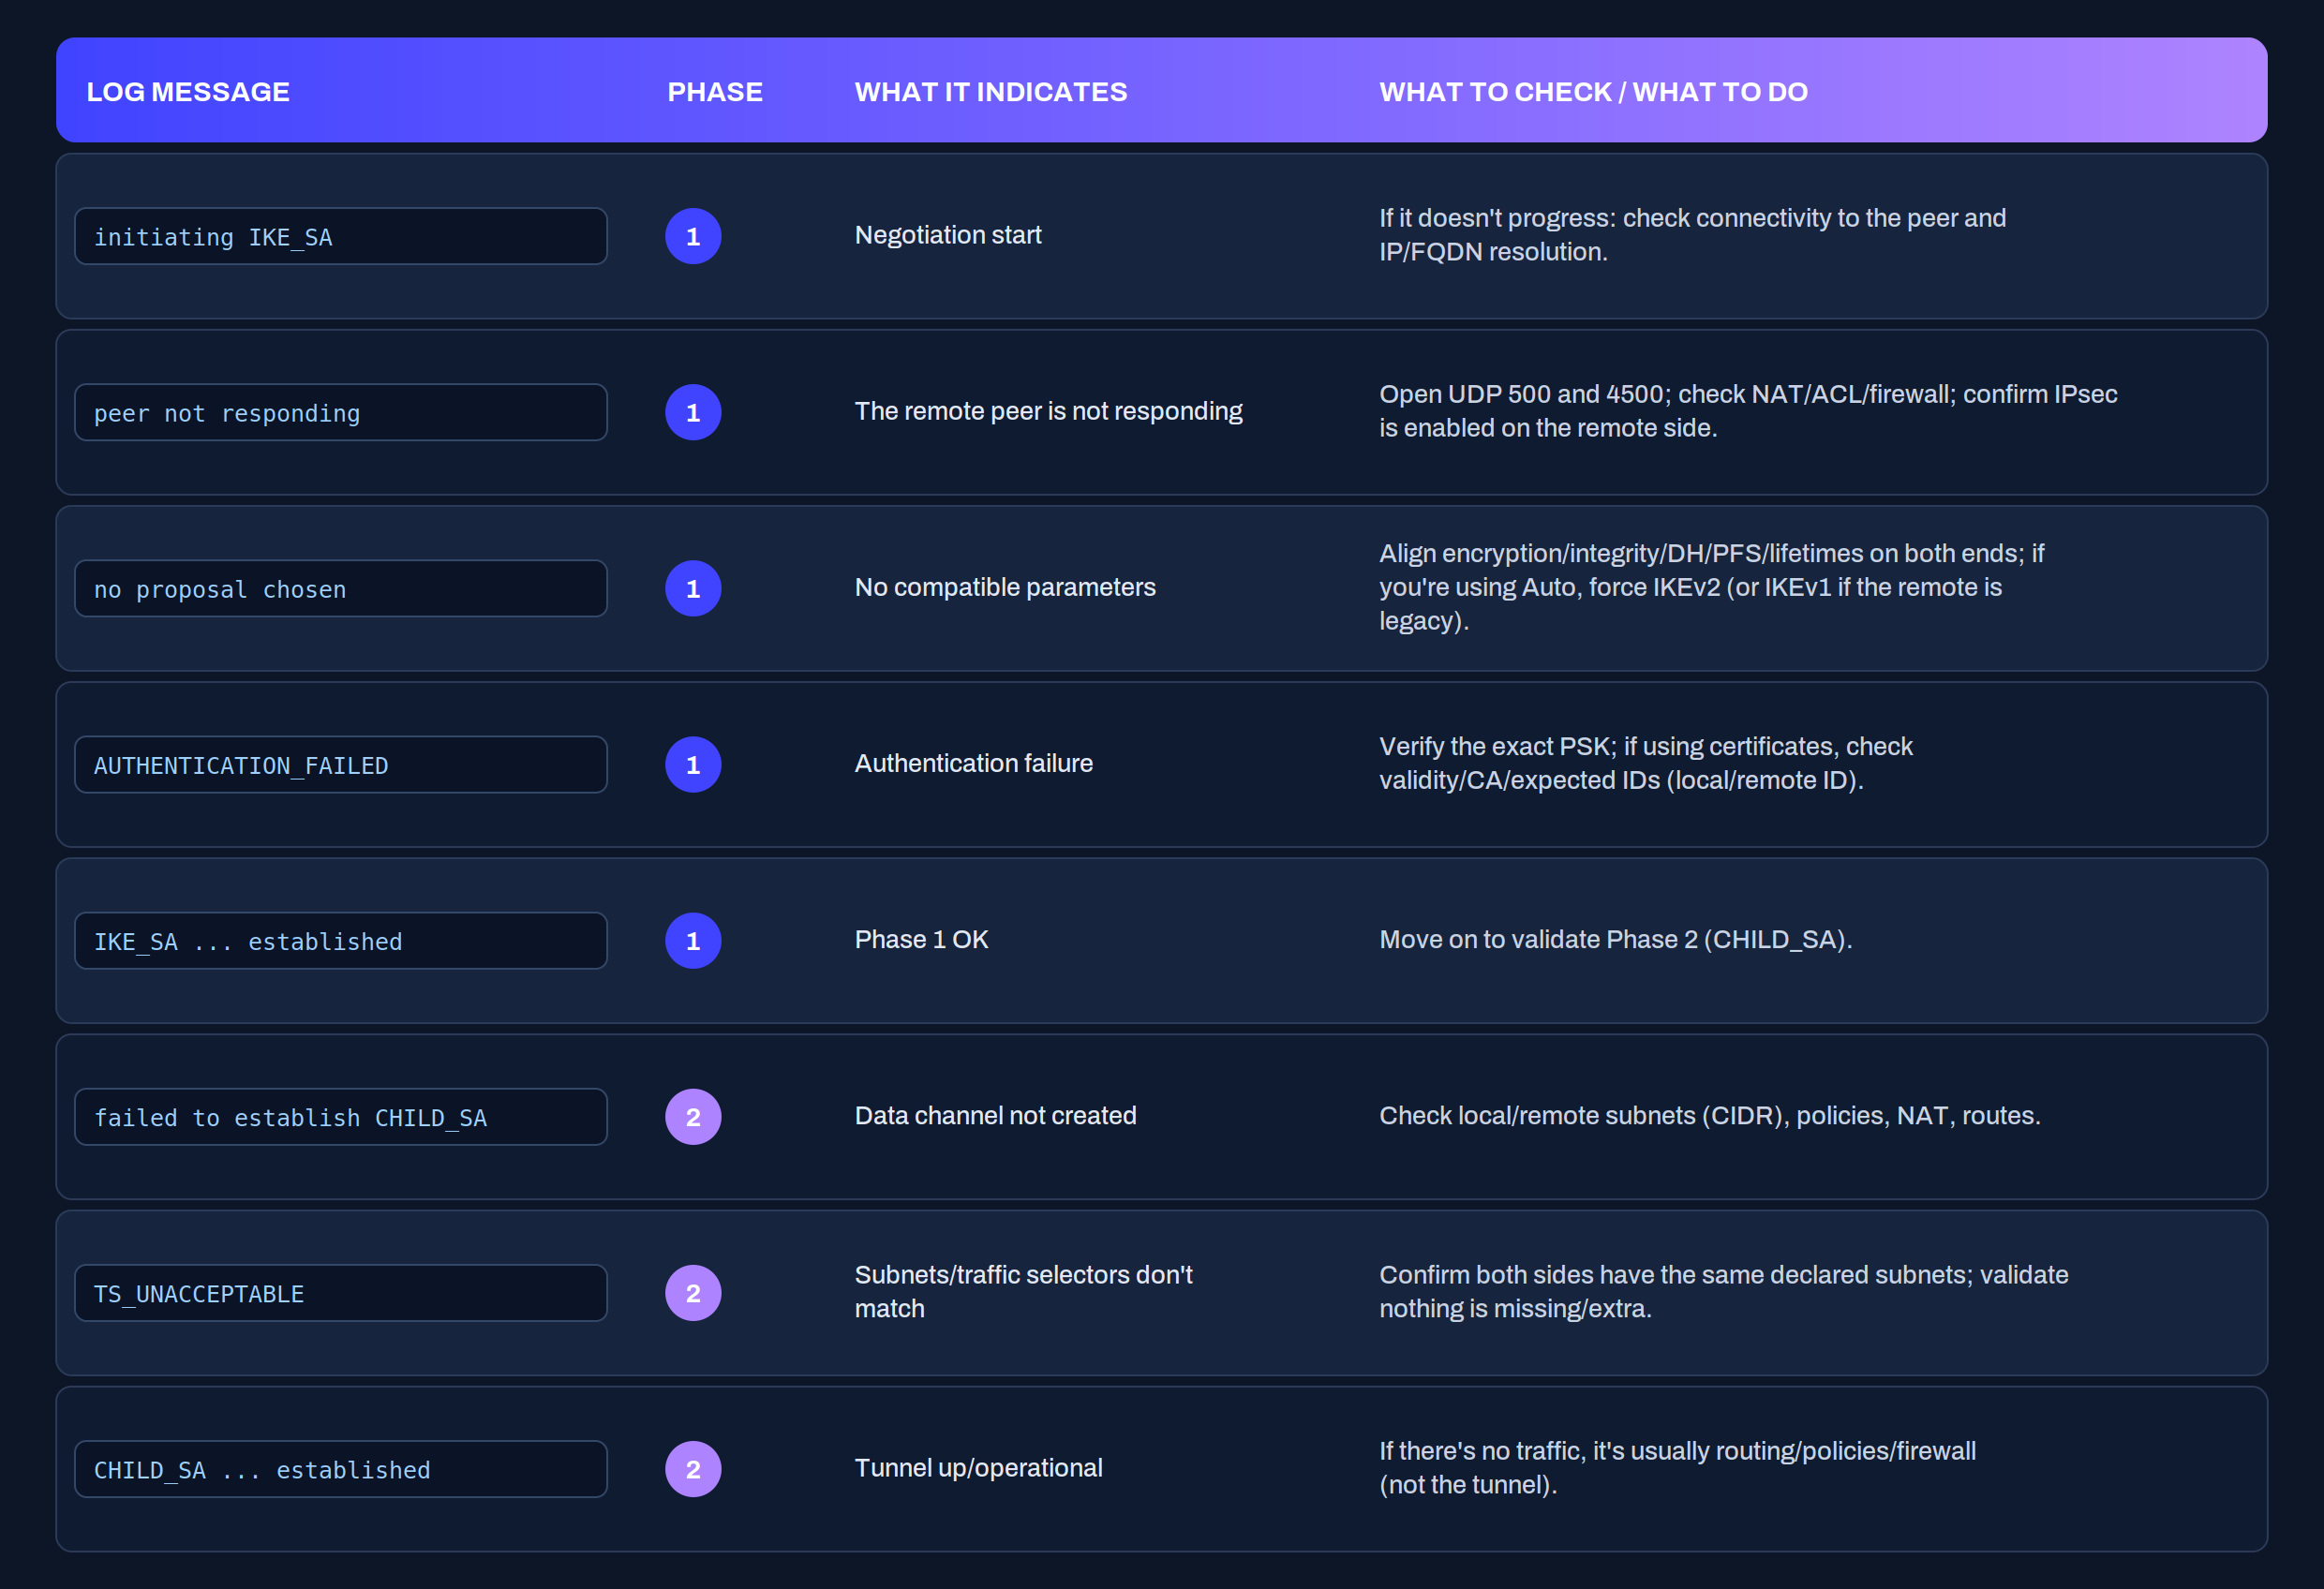
### Interpret the log messages
### Diagnosis checklist
1. Generate logs and look for `error`, `failed`, `proposal`, `AUTH`, `TS_`.
2. Does `IKE_SA ... established`appear? **not**, you have a Phase 1 problem (you may see `initiating IKE_SA` without it going any further). If **yes**, continue.
3. Does `CHILD_SA ... established`? If you see `failed to establish CHILD_SA`, it is usually networks, routes, or firewall (Phase 2). If **yes** appears, the tunnel is fine; if there is still no traffic, look at routes and policies, not the tunnel.
4. `peer not responding` → check UDP 500/4500 and firewall/NAT.
5. `no proposal chosen` → there are mismatched settings (ciphers, groups, lifetimes).
6. `AUTHENTICATION_FAILED` → check the key (PSK) or certificates and IDs.
7. `TS_UNACCEPTABLE` → check that the subnets match exactly on both sides.
### Check from the client side
The logs tell you the phase; these commands confirm the cause from a server on your network.
For Phase 1, check connectivity with the peer and that the IPsec ports are open. On Linux:
```bash
ping
nc -vzu 500
nc -vzu 4500
```
On Windows, basic connectivity from PowerShell (UDP ports 500/4500 must be open in the firewall and NAT on both sides):
```powershell
Test-NetConnection
```
For Phase 2, check that you can reach the remote subnet and that there is a route to it:
```bash
ping
ip route
```
```powershell
route print
```
### When to escalate to Partner Success
If after these steps you are still stuck, the Partner Success team will help you. To resolve it as quickly as possible, send:
* **From the log**: the first error that appears, 20-30 lines before and after to see the context, and the timestamps exactly as they appear.
* **From the tunnel**: IKE version (v1/v2/Auto), peer IP or FQDN, local and remote subnets in CIDR, whether there is NAT or a firewall in between, and the exact time of the test.
Since logs rotate by size, reproduce the failure and generate the logs right after: that way the file contains exactly what needs to be checked.
### Conclusion
With the troubleshooting console you go from "the VPN isn't working" to "it fails in Phase 2 because the subnets do not match" in minutes. The method is always the same: locate whether you get to `IKE_SA established` and to `CHILD_SA established`, and that tells you whether to look at the initial connection or the data transfer. From there, the table and the commands lead you to the cause.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.plenit.com/docs-en/productos/servers/how-to/vpn-logs-and-troubleshooting.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.