

How to Create a VPC and Associate a TIER in Plenit
A VPC lets you organize the network of your Servers environment into separate subnets, the TIERs.
In this tutorial, you create a VPC and associate its first TIER with it, the basis for layering segmentation (application, database) or for later setting up a VPN between networks.
👍 What you get
A VPC network created and with an associated TIER, ready for you to attach your servers to it and define access from the outside.
What a VPC is and what a TIER is
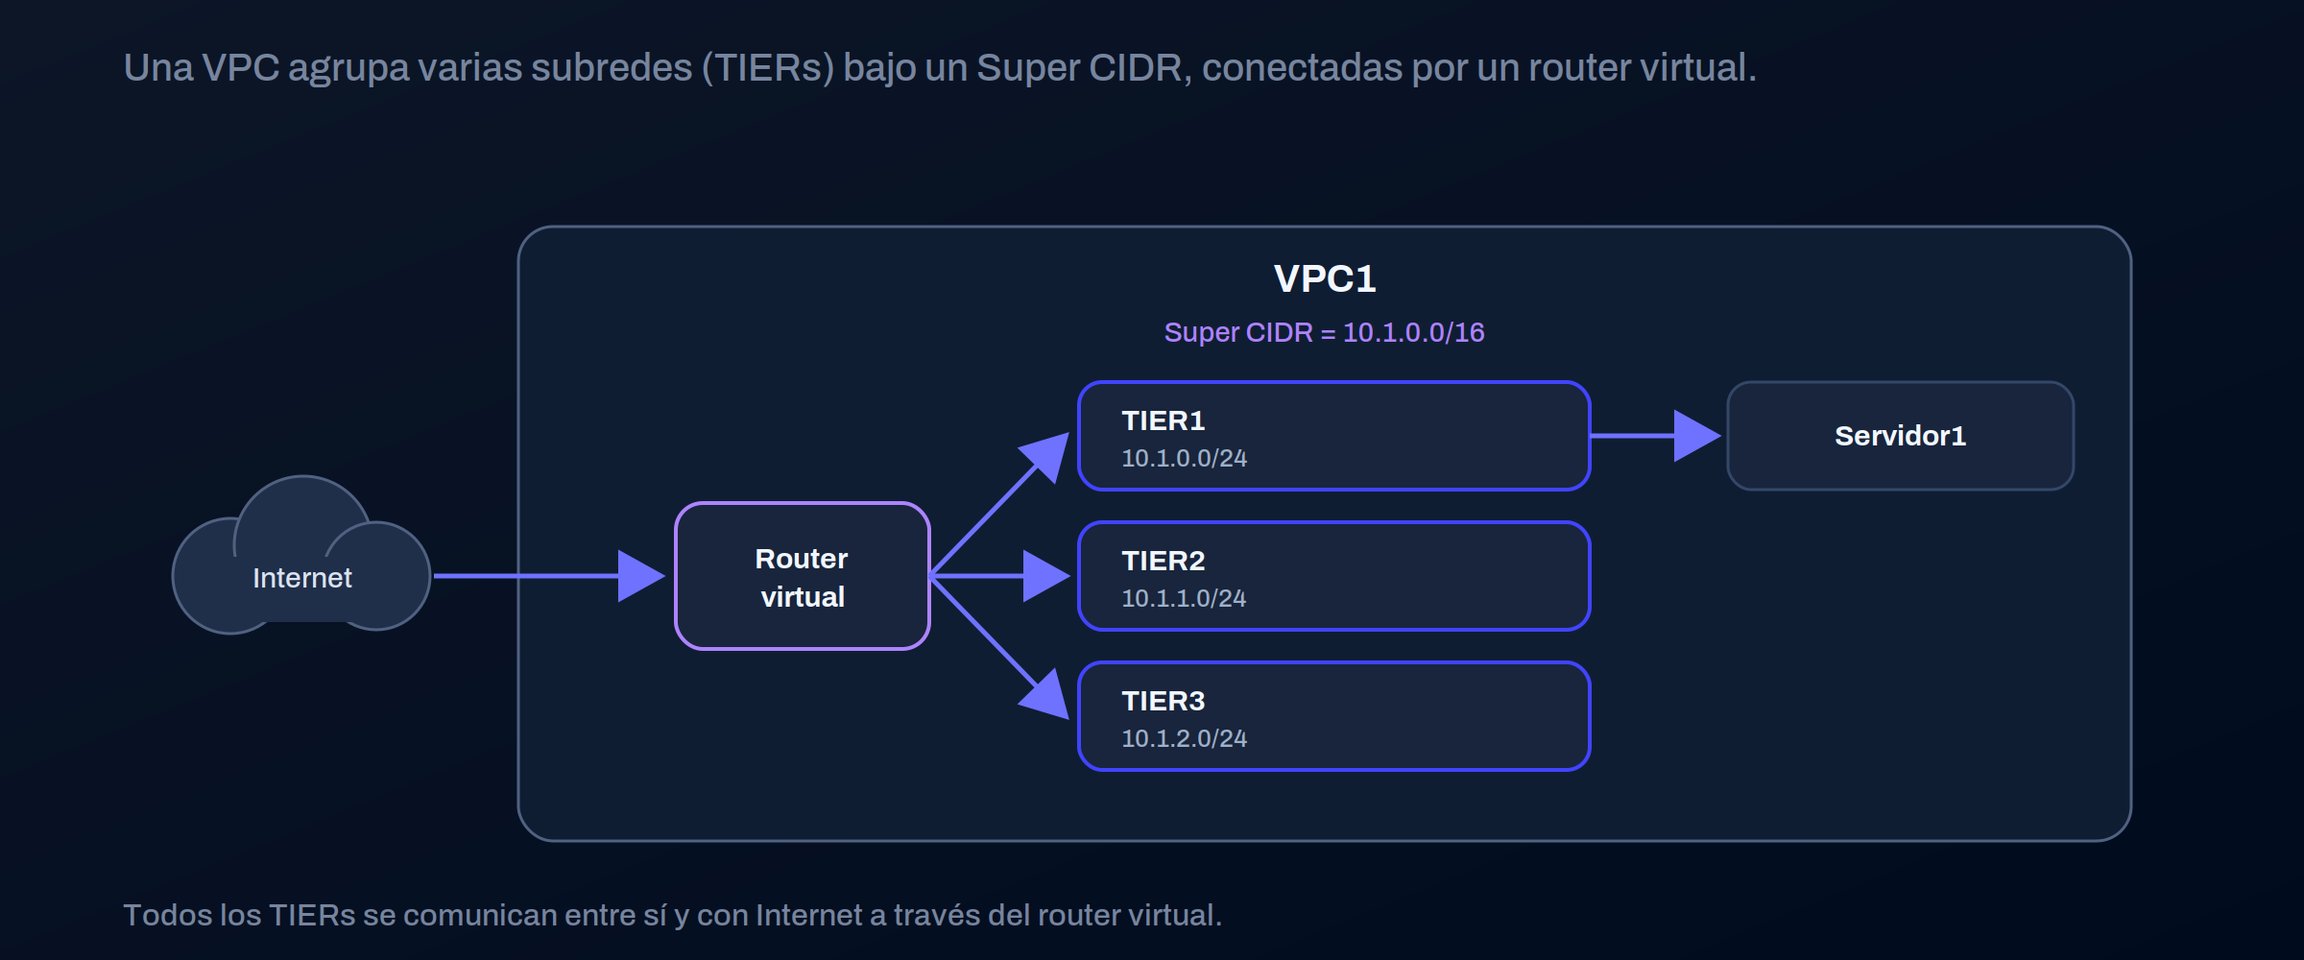
A VPC is defined with a Super CIDR, the main network that contains all subnets. Each subnet is a TIER, which corresponds to a VLAN. All the TIERs of a VPC communicate with each other and with the Internet through a virtual router.
Super CIDR
The VPC's global range, within which the TIERs live (for example 10.1.0.0/16)
TIER
A subnet within the VPC (for example 10.1.0.0/24)
Virtual router
What connects the TIERs to each other and to the Internet
📘 Why segment into TIERs
Separating the application layer from the database layer into different TIERs lets you control what talks to what, instead of having everything on a flat network.
A VPC supports up to three TIERs on the same virtual router.
Before you start
Have an active Servers subscription.
If you don't have one yet, deploy a server first: Deploy your server.
Step 1. Access the Servers subscription
Enter the Servers subscription from its card in the service.
{/* 📸 SCREENSHOT 1 · Servers subscription card */}

Step 2. Open Network/IP and create the VPC network
In the left sidebar menu, open Network/IP, select VPC Networks and click Create VPC network.
{/* 📸 SCREENSHOT 2 · left menu Network/IP > VPC Networks with the Create VPC network button */}

Step 3. Name the VPC
Enter a name to identify it easily, for example VPC1. If you leave it blank, we'll generate it automatically. Click Continue.
{/* 📸 SCREENSHOT 3 · VPC name field and the auto-generated Super CIDR highlighted */}

📘 The Super CIDR, auto-generated but yours
We generate the Super CIDR automatically, but you can change it. If you do, note down the range: the TIERs you create later have to fit within it.
Step 4. Add and name a TIER
When the VPC is created, you'll see a notice that it still doesn't contain any TIERs. Click the three dots on the VPC and choose Add Tier. Enter a name, for example TIER1. If you leave it blank, we'll fill it in for you.
The platform assigns a range by default 10.1.0.0/24, which is contained within the Super CIDR 10.1.0.0/16. When you're done, the VPC and its TIER appear in Networks/IP → VPC Networks.
{/* 📸 SCREENSHOT 4 · three-dot menu with "Add Tier" and the TIER name field */}

👍 Use clear names from the start
Naming VPCs and TIERs well (by function or by layer) saves you time when the network grows and you need to know at a glance what each thing is.
Verify the network from a server
When you connect a server to the TIER, confirm from inside that it has received the correct IP and gateway.
On Linux:
On Windows, from PowerShell or CMD:
To check connectivity with another server on the network, run ping to its IP. On Windows, the firewall blocks incoming ICMP by default, so allow it on the destination server with an inbound rule:
Plan your ranges before growing
The biggest oversight when setting up multiple VPCs is overlapping ranges, which breaks routing as soon as you connect them. Reserve a different Super CIDR per VPC from the start.
Super CIDR
10.1.0.0/16
10.2.0.0/16
Example TIER
10.1.0.0/24
10.2.0.0/24
Next steps
To connect two VPCs, create a second one (for example
VPC2with10.2.0.0/16, without overlapping) and bring up the tunnel: How to create a site-to-site VPN tunnel.The VPC is the only network type with site-to-site IPSec VPN, and you can connect it with VPCs from other cloud providers or with compatible equipment (Cisco ISR with IOS 12.4 or higher, Juniper J-Series routers with JunOS 9.5 or higher).
To review the network types: Server networking.
Last updated
Was this helpful?